Telecommunications security frameworks continue to evolve as mobile operators face increasingly complex signaling environments spanning legacy networks, 5G, cloud-native infrastructure and satellite-to-mobile connectivity.
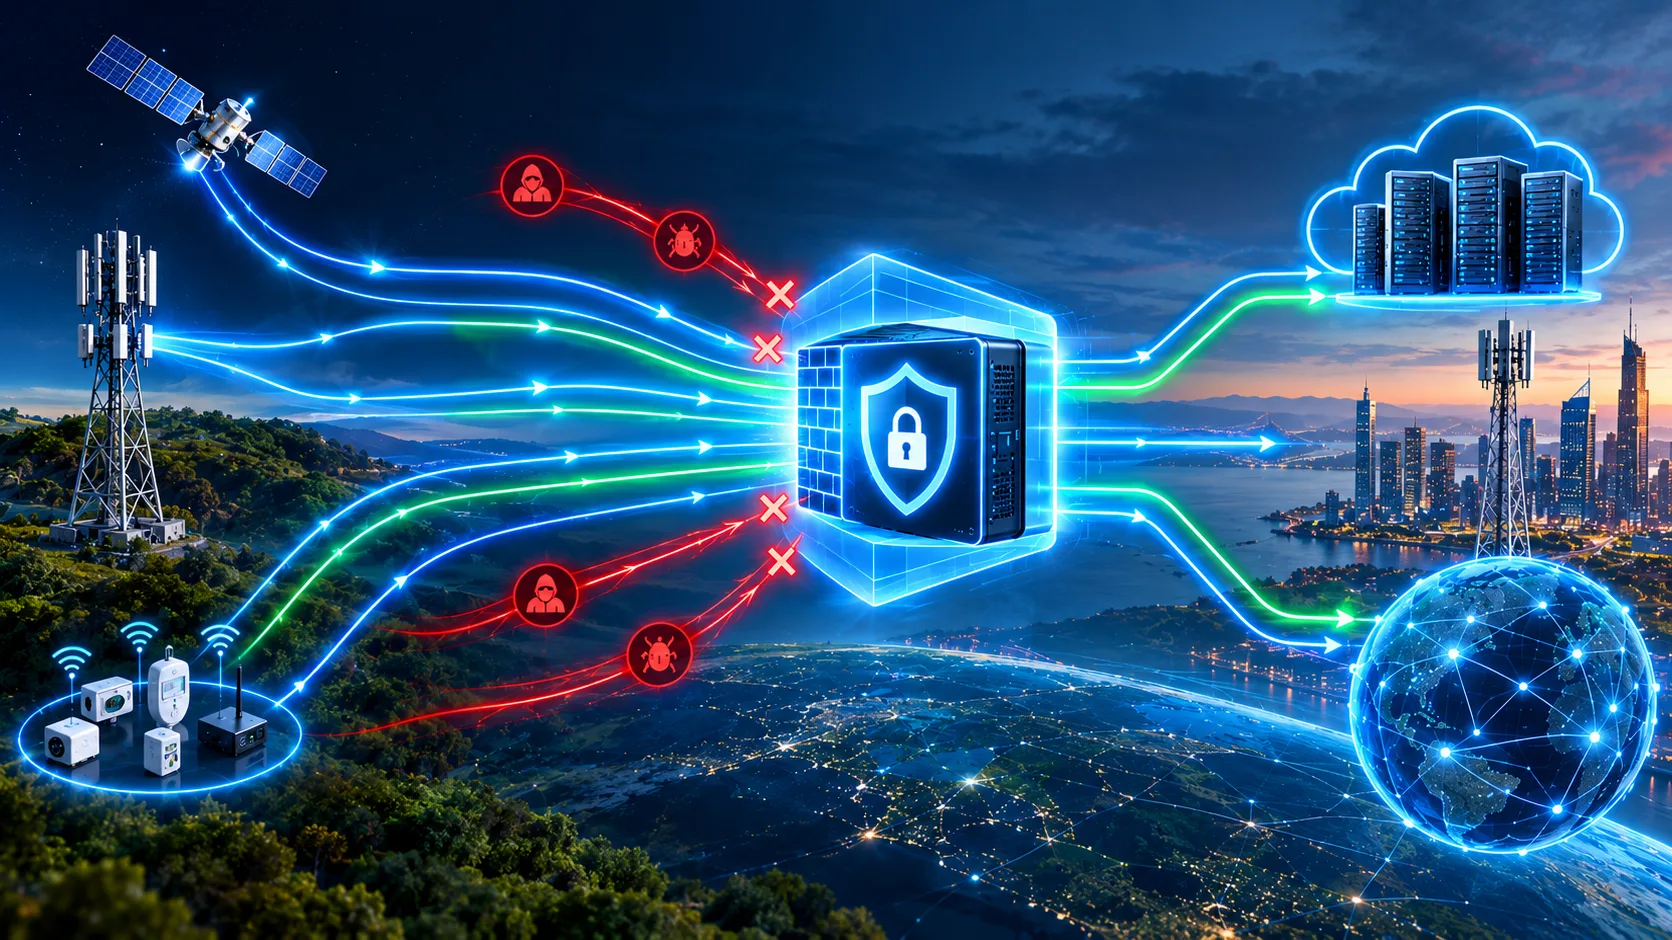
The Shift Towards Layered Signaling Security
The UK’s revised Telecommunications Security Code of Practice, version 1.1, issued in July 2026, reinforces the importance of proportionate, risk-based security controls. Its guidance specifically addresses outgoing signaling traffic, recommending that providers check for evidence of compromise or attempts to bypass existing security mechanisms. It also recommends considering an independent signaling Intrusion Detection System (IDS), ideally independent of an existing signaling firewall.
This distinction is important. A signaling firewall enforces security policies by filtering or blocking messages that violate defined rules. An independent IDS provides a complementary layer of monitoring, helping operators identify suspicious activity and potential weaknesses or bypasses in existing controls.
For mobile network operators, the objective is not simply to deploy additional security appliances. It is to establish appropriate visibility, control and monitoring at the network interfaces where signaling traffic enters, leaves and moves between trusted and untrusted domains.
Integrating Signaling Security with Core Routing
BroadForward addresses these requirements through its converged signaling software platform, integrating routing, interworking and protocol-specific security capabilities within a common architecture.
Its portfolio includes SS7 Firewall and Diameter Firewall capabilities, alongside 5G security functions such as the Security Edge Protection Proxy (SEPP). Its Service Communication Proxy (SCP) supports service-based communication and routing within the 5G core, while the SEPP protects signaling exchanged between mobile networks across the 5G roaming boundary.
These functions address distinct security and routing requirements. When deployed appropriately, integrated signaling controls enable operators to apply protocol-specific policies at relevant interconnect boundaries while simplifying the management of signaling infrastructure.
Integration does not eliminate the need for complementary monitoring, independent detection where appropriate, security testing and incident response. Instead, it provides a foundation on which operators can build a layered defense around the protocols and interfaces relevant to their networks.
A practical example is BroadForward’s live deployment with Terrestar Solutions. Announced in October 2026, the deployment includes BroadForward’s Diameter Routing Agent/Diameter Edge Agent (DRA/DEA) and Diameter Firewall in Terrestar’s network, supporting signaling between satellite and terrestrial mobile network environments.
The deployment demonstrates the application of routing and protocol-specific security controls to satellite-to-mobile interworking. It also illustrates how signaling security is becoming relevant to an increasingly diverse connectivity ecosystem. It should not, however, be interpreted as evidence that signaling controls alone can protect against every threat affecting connected devices or satellite infrastructure.
GSMA Guidance and Protocol-Aware Security
Industry guidance provides an important reference for securing telecommunications signaling interfaces. The GSMA’s security document portfolio includes:
- FS.11 — SS7 Interconnect Security Monitoring and Firewall Guidelines: recommendations for SS7 interconnect monitoring and firewall controls.
- FS.19 — Diameter Interconnect Security: guidance on Diameter-related threats and countermeasures.
- FS.21 — Interconnect Signalling Security Recommendations: broader recommendations for interconnect signaling security.
- FS.36 — 5G Interconnect Security: guidance addressing security threats and countermeasures associated with 5G interconnection.
These documents support a protocol-aware approach to signaling security. Their recommendations should be distinguished from binding legal obligations, which depend on the applicable jurisdiction, regulatory framework and contractual requirements.
The wider technical direction is also reflected in ITU-T Recommendation Q.3066, approved in January 2026, which addresses principles for detecting and mitigating signaling attacks across telecommunications protocols.
Together, these resources underline the importance of understanding signaling behavior, filtering unauthorized messages, monitoring anomalous activity and accounting for threats that span multiple protocols or network generations.
For operators managing SS7, Diameter and 5G service-based architectures, this means security controls must reflect the specific protocols, interfaces and trust relationships present in their networks.
Satellite Connectivity and Cellular IoT Expand the Security Challenge
The integration of non-terrestrial networks (NTNs) with terrestrial mobile infrastructure introduces additional interconnection scenarios. Satellite operators, mobile network operators and connectivity providers must support signaling exchanges across different network architectures while maintaining appropriate routing, security and operational controls.
Terrestar Solutions provides a real-world example of this evolution. Its deployment of BroadForward’s DRA/DEA and Diameter Firewall supports signaling between satellite and terrestrial mobile network domains, helping enable connectivity across Canada, including areas with limited terrestrial coverage.
Meanwhile, the cellular IoT market continues to expand. Fortune Business Insights forecasts that the global cellular IoT market will reach approximately US$53.24 billion by 2034. This figure represents a market-value forecast, not a forecast of the number of connections or the incidence of cyberattacks.
A growing and increasingly diverse connectivity ecosystem creates additional operational challenges. Operators must accommodate different device capabilities, network technologies, roaming relationships and interconnection models. Effective visibility, consistent policy enforcement and coordinated incident response consequently become important elements of network resilience.
AI-enabled threats add another consideration. Research into autonomous AI agents and malware-like behavior highlights the potential for emerging technologies to automate aspects of cyberattacks and adapt to unfamiliar environments. However, experimental demonstrations involving simulated or controlled environments should not be presented as proof of autonomous malware spreading through real-world cellular IoT networks.
The practical implication is that operators should prepare for evolving threats across connected devices and the networks supporting them. Device hardening, access controls, traffic analysis and endpoint protections, where available, remain important alongside signaling security.
Building Resilience Through Complementary Security Controls
For mobile network operators, IoT connectivity providers and satellite service providers, signaling security is one component of a broader defense strategy.
Signaling firewalls enforce protocol-specific policies at appropriate network boundaries. Routing and interworking functions manage exchanges between network domains, while independent monitoring can provide additional visibility into anomalous activity and potential security-control bypasses.
These capabilities should complement device security, network monitoring, vulnerability management, security testing and incident response. No single signaling control can prevent every attack, particularly threats originating on compromised devices or targeting systems outside the signaling plane.
BroadForward’s converged signaling architecture brings routing, interworking and supported security functions together within a common software platform. Its deployment in satellite-to-mobile connectivity demonstrates how these capabilities can be applied to emerging interconnection models.
As telecoms security frameworks evolve and networks become more interconnected, the priority is to combine effective protocol-aware controls with independent detection where appropriate. This layered approach helps operators maintain visibility, protect signaling interfaces and support resilient connectivity across legacy, 5G, cloud-native and non-terrestrial network environments.