

Bridging the Skies: How Signaling Unlocks the Satellite-to-Mobile Revolution Read newspost
5G Traffic Growth Accelerates as India Closes the Gap with 4G Read newspost
6G Core Debate Raises Familiar Questions About Standards and Evolution Read newspost

SS7 Firewall (SS7FW)

Protect your 2G and 3G core networks with the BroadForward SS7 Firewall. Serving as the defense shield for 2G-3G signaling, it delivers deep application-layer (MAP/INAP) inspection, real-time location/velocity tracking, and full GSMA FS.11 compliance, powered by BroadForward’s award-nominated firewall technology to protects 2G-3G networks against possible attacks, unauthorized senders, malformed messages, overload situations, and much more.

Deployment options:

  • Bare metal Bare metal
  • Virtual machine Virtual machine
  • Container Container
  • Cloud Cloud

Features:

  • GUI based firewall rules enablement and configuration
  • Follows GSMA FS.11 recommendations
  • Transparent mode for non-blocking trail of firewall rules
  • UE-tracking for cat.3 location/velocity plausibility determination
  • Can be combined with Gateway-STP service

Foundation

The BroadForward SS7 Firewall in your Network

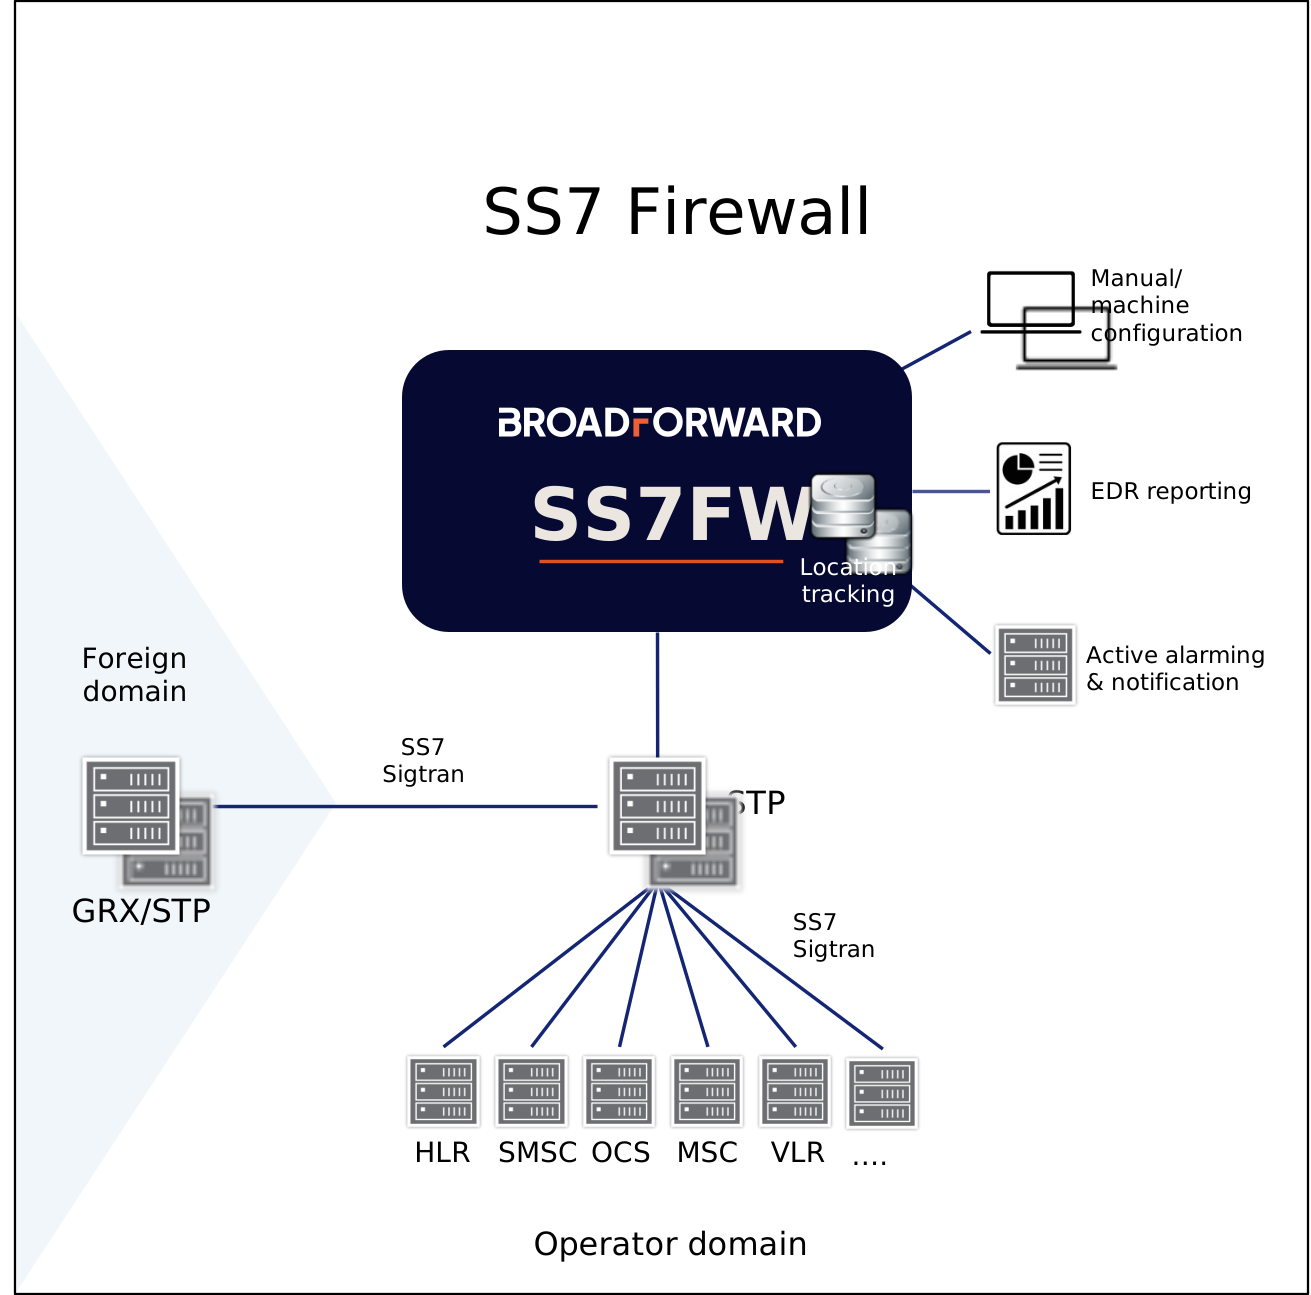
The BroadForward SS7 Firewall (SS7FW) is the network’s active security and enforcement layer for all SS7 (MAP/CAP/INAP) signaling across circuit‑switched domains. It establishes a centralized, security perimeter that continuously inspects, filters, and governs national and international SS7 interconnect traffic, protecting 2G-3G networks from malicious requests, spoofing, location‑tracking exploits, roaming abuse, denial of service (DoS), and unauthorized data extraction.

The SS7FW is part of BroadForward’s signaling security portfolio, recognized across the industry with its GSMA GLOMO‑nominated firewall engine and Champion status in Kaleido Intelligence’s Roaming Vendor Hub 2025–2026 (ranking among the top 16 vendors out of 80). It enables operators to gain full visibility and control over SS7 security, ensuring that every inbound and outbound message adheres to strict trust, policy, and threat‑mitigation rules.

Years of BFX USC in production
0
Operators running BFX USC
0 +
GSMA GLOMO winner
0 x

Trusted by

liberty-global
2DEGREES
AIRALO
ALIANZA
ARELION
ATOS
BICS
CELLUSYS
CGI
CIRRUS
CLARO
COMFONE
DIGICEL
DOCOMO
EMIRCOM
ENGHOUSE
ETISALAT
IBASIS
ICONECTIV TNS
LEBARA
M1
MOBIFONE
MODULO
MTN BYOBAB
NGVOICE
NOMIOS
NSSOL
NTT
ODINE
ORANGE
POLKOMTEL
PROXIMUS
SAMSUNG
TATA
TELENET
TELKOMSEL
TELMEX
TERRESTAR
TURK TELEKOM INTL
UNITEL
VODAFONE

Multi-tenancy

Defending Legacy Core Infrastructure: Signaling Protection

Every BroadForward product runs on the BFX USC - one engine, one operational model. Adding and working with new 2G–5G signaling functions is straightforward because all BroadForward products use the same GUI, provisioning model, workflows, and operational environment - one interface for all signaling.

Features a 100% graphical interface (CLI is also supported) with flexible templates for configuring custom security policies, MAP/CAP/INAP application layer inspection rules, and threat mitigations without vendor coding dependency or expensive CR fees.

Built on BroadForward’s GSMA GLOMO nominated firewall engine and backed by the BroadForward’s Champion status in Kaleido Intelligence’s Roaming Vendor Hub - acknowledging BroadForward’s leadership in signaling security.

BroadForward SS7FW

Trusted by professionals

See why leading professionals choose BroadForward.

We’re proud to have been leveraging the BroadForward platform for quite a while. The solution has played an important role in enabling connectivity with operators and providers preparing for the 5G SA era. Its flexibility, reliability, and future-ready architecture make it a standout platform in the industry.

This not only saves money, but critically speeds time to market

An elegant and innovative solution to a legacy problem of critical voice networks — fulfils an immediate market need

One of the few independent signaling experts successful in winning business from operators looking for a multi-technology signaling platform

BroadForward’s solutions have already strengthened our signaling capabilities, driving greater operational efficiency

Specifications

Everything you need to evaluate, in one place

Supported Standards & Core Features

  • GSMA FS.11 SS7 Security Guidelines Fully compliant with GSMA FS.11 standards, enforcing Category 0, 1, 2, and 3 screening rules for inbound and outbound SS7 traffic.
  • Deep MAP/CAP/INAP Message Inspection Performs stateful Layer 3 through Layer 7 inspection of MTP3, SCCP, TCAP, MAP, CAP, and INAP parameters, opcodes, and subscriber identity fields in real time.
  • Anti-Spoofing & Location Tracking Defense Detects and blocks illegal subscriber location queries (AnyTimeInterrogation, ProvideSubscriberInfo, SendRoutingInfo), IMSI harvesting, and spoofed SMS traffic.
  • Global Title (GT) & MAP Screening Validates GT calling/called party address consistency, SCCP routing indicator verification, and MAP application context validity before traffic enters the home core.
  • Script-Free GUI Security Rules Engine Provides a 100% graphical environment to build, test, and activate custom security rules, AVP filters, and threat mitigations without writing code or paying vendor CR fees.
  • Efficient & Cloud‑Agnostic Architecture Designed for low-latency, cloud-native deployment on Kubernetes-based or Red Hat OpenShift container environments, virtual machines, or bare-metal edge nodes.
  • Unified Security Suite 2G/3G/4G and 5G Firewall support in a single software engine running on the GSMA award winning BroadForward BFX Unified Signaling Core (USC) platform.

Extended Features

  • Velocity Tracking & Time-Distance Plausibility Detects implausible subscriber location jumps across international borders to stop SIM swap fraud, service/billing abuse, and mobile identity theft.
  • Transparent Mode Support New security rules can be introduced in transparent mode, where they are evaluated and logged but do not block traffic until fully validated.
  • Rate Limiting Selective Ingress Throttling Features selective rate limiting and volume threshold monitoring to mitigate signaling storms, scanning campaigns, and attacks on legacy HLR/VLRs.

Get more product information

Request the latest data sheet for the BroadForward SS7 Firewall and share it with your security team for a complete technical overview.

  • Full technical specifications and security feature list
  • Deployment topology and multi-generation firewall integration overview
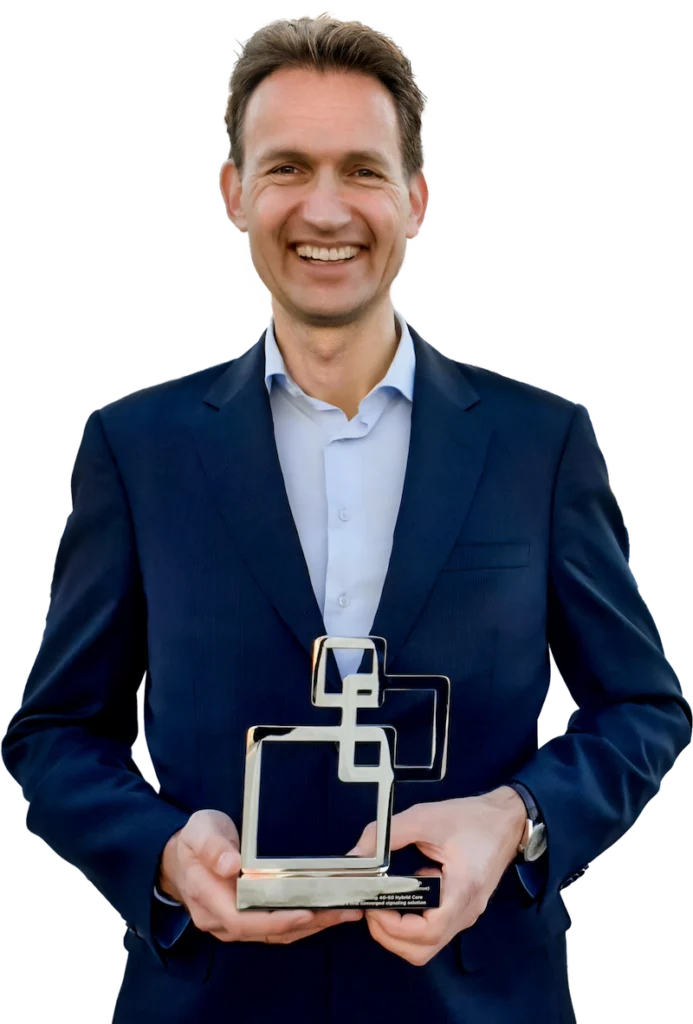
A person in a suit smiles while holding a BroadForward GLOMO award.

FAQ

We are happy to help you with any questions.

Deployment

Freedom of Environment: Deploying Where it Makes Sense

With the BFX Unified Signaling Core (USC) at its foundation, operators are not tied to a specific hardware vendor, appliance cycle, or hyperscaler. The BroadForward SS7 Firewall can be deployed or migrated across virtual machines, containers, or bare metal, using the same configuration, without re engineering. Because the BroadForward SS7 Firewall separates the underlying execution platform from its threat inspection rules, state tables, and security profiles, moving environments requires no re-engineering. All firewall inspection logic, GSMA FS.11 screening rules, screening tables, and cross-protocol layer correlation rules built in the GUI can be exported as clean, platform-independent configuration files.

Bare metal

Maximum performance on existing server hardware. No hypervisor overhead.
Bare metal

Virtual machine

Deploy on your current hypervisor. Full HA and geo-redundancy supported.
Virtual machine

Container

Kubernetes-orchestrated. Automated lifecycle management. Scales horizontally.
Container

Cloud

Public, private, or hybrid. Scales without re-architecture as your network grows.
Cloud
Search

Change language